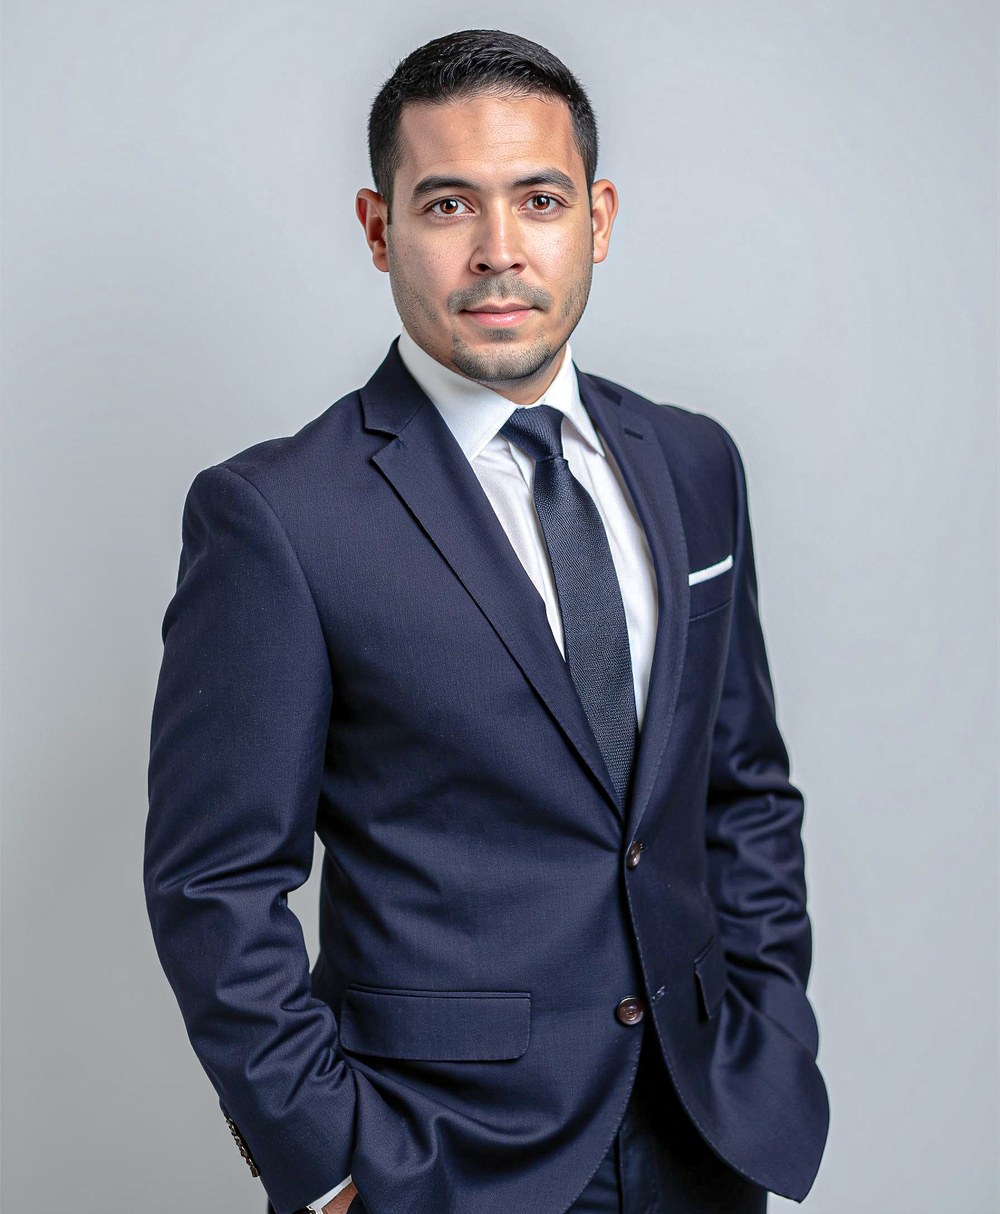
Zero Trust, Without the Buzzwords
What “never trust, always verify” actually means for a regulated organization with a small security team.
Zero Trust & Risk Advisor · Annapolis, Maryland
Erick Ramos is a U.S. Marine Corps veteran and cybersecurity advisor, helping regulated enterprises in healthcare, finance, and SLED assume breach, verify every request, and understand which risks actually matter — so zero trust becomes a practical, prioritized roadmap instead of a buzzword.
7+
Years in Cyber
42
Courses & Certs
USMC
COMSEC Veteran
About
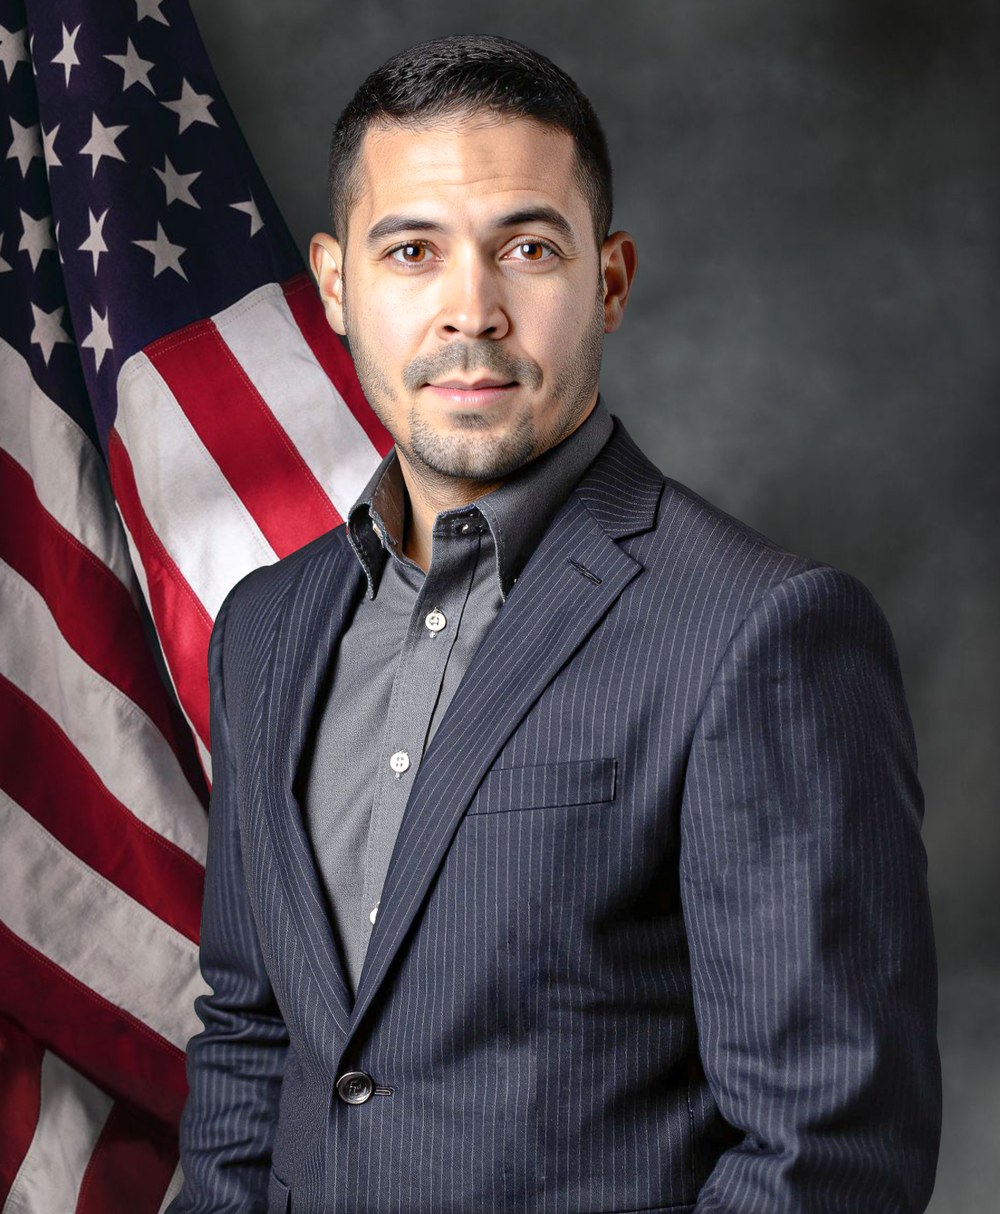
Erick Ramos has spent the last 7 years in cybersecurity, backed by over 16 years of progressive sales experience. As a cybersecurity advisor focused on zero trust and risk awareness, he helps regulated organizations — across healthcare, finance, and SLED — stop implicitly trusting users, devices, and networks, and make clear-eyed decisions about the risks that matter most.
The perimeter no longer holds, and attackers increasingly log in rather than break in. A zero trust approach — verify explicitly, grant least privilege, assume breach — only works alongside risk awareness: knowing what is exposed, what is actually being exploited, and where people are the weakest link. That visibility is the starting point for continuous, unified exposure management.
A proud veteran of the U.S. Marine Corps, Erick served during Operation Enduring Freedom in the aftermath of 9/11 as a Radio Operator specializing in communications security (COMSEC) and cryptographic codes — a foundation of discipline around verifying before trusting that still defines how he approaches security today.
Erick is an active member of the Cybersecurity Association (formerly the Cybersecurity Association of Maryland) and serves as a trusted Security and Risk Advisor to regional small and medium-sized businesses. He also publishes a weekly threat intelligence brief tracking CISA KEV additions and the defensive priorities that follow.
Alongside security, Erick builds with AI — using Claude Code, ChatGPT Codex, and other tools to develop applications and automate his own workflows. See AI & Automation.
Having led and mentored high-performing teams of Account Executives, Account Managers, and Sales Engineers, Erick translates complex risk and zero trust concepts for both technical and business stakeholders — turning findings into decisions leadership can act on.
Verticals Served
Core Expertise
Anchored by one principle — never trust, always verify — with risk visibility, exposure management, detection, and data protection built around it.
Zero trust replaces implicit trust with continuous verification: every user, device, and request is checked, every account gets only the access it needs, and every environment is designed as if a breach has already happened. Risk awareness keeps it honest — giving security leaders a clear, prioritized view of what is exposed, what is actually being exploited, and where people and process add risk.
AI & Automation
Erick treats AI as a working tool, not a talking point — using it to build software, speed up his own work, and automate the repeatable parts — and brings a security advisor’s eye to how it’s used.
Builds and ships applications with AI coding agents — including Claude Code and ChatGPT Codex, alongside other AI development tools — from first idea to working software. Current project: Void Frontier, a real-time strategy (RTS) game in development, built with Claude.
Uses AI every day for research, writing, analysis, and planning — and has completed training in Everyday Productivity with Claude Cowork and Strategic Prompt Engineering.
Builds automations for sales and CRM work and for reporting, taking repetitive tasks off the plate so more time goes to conversations and decisions. Every automation keeps a human in the loop — it drafts and recommends, a person reviews and approves — and is built with security in mind, with deliberate care for credentials, permissions, and data access.
This website was built with AI, not the older playbook of hand-coding every page, stacking plugins on a heavyweight CMS, or waiting in a developer queue. No database, no plugin sprawl: just fast static pages and a small custom tool. It’s a working example of where web development is headed.
Threat Intelligence
A weekly read on what's actually being exploited — CISA KEV additions, actively exploited vulnerabilities, and the defensive priorities that follow — plus field notes on zero trust, risk, and exposure management.
Seven vulnerabilities hit CISA's KEV catalog Sept. 13–20 — including a CVSS 10.0 Cisco ISE bypass and three Linux kernel flaws.
Sept. 21, 2026 · ~14 min read
Weekly Cyber Intelligence14 vulnerabilities hit CISA's KEV catalog Sept. 6–13 — double the prior week — spanning edge devices, developer platforms, and a new AI warning.
Sept. 14, 2026 · ~17 min read
What “never trust, always verify” actually means for a regulated organization with a small security team.
Why a CVSS score alone misleads — and how to rank exposure by what attackers are actually exploiting.
Sanctioned or not, AI usage is happening inside your org right now. Here's how to find it.
Continuing Education
Cybersecurity · 35 (zero trust & risk awareness highlighted)
Sales & Professional Development · 7
Cybersecurity continuing education via Cybrary and CompTIA.
Contact
Whether it's a zero trust conversation, a risk review, a platform health check, or an advisory engagement — drop a line and I'll get back to you within one business day.
Mon–Fri: 9am – 6pm
Saturday: 9am – 12pm
Sunday: Closed